
Artificial intelligence has moved beyond the experimental phase. Across the United Kingdom, software companies are embedding AI into recruitment platforms, financial services, healthcare applications, legal technology and customer support systems at an unprecedented pace. Yet as investment accelerates, so too does regulatory scrutiny.
Unlike the European Union, which has chosen a comprehensive legislative route through the AI Act, the United Kingdom has continued to pursue a distinctly British approach: encouraging innovation while relying on existing regulators to oversee AI within their respective sectors. For technology founders, this creates both opportunity and complexity. There is no single “AI law” to comply with, but there are numerous legal obligations that collectively shape how AI products should be designed, deployed and governed.
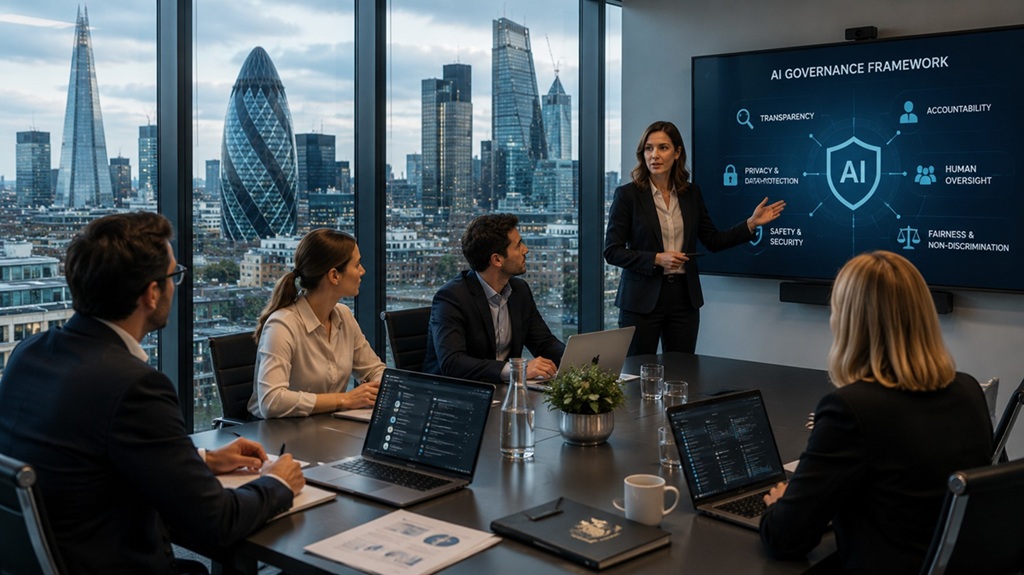
In 2026, many early-stage companies are discovering that enterprise customers and investors now ask a different set of questions. Rather than asking whether a product uses artificial intelligence, procurement teams increasingly ask whether it has been assessed for bias, whether customer data is protected, whether decisions can be explained and who ultimately remains accountable when AI makes mistakes.
The consequence is clear: AI governance has become a commercial requirement rather than simply a legal consideration.
A Different Regulatory Philosophy
Since leaving the European Union, successive UK governments have resisted introducing an overarching AI Act similar to that adopted in Brussels. Instead, policymakers have favoured what is often described as a principles-based, sector-led framework.
This philosophy rests on a simple assumption. AI is not a single technology applied in a single industry. The risks associated with an AI-powered medical diagnostic system differ substantially from those presented by an automated marketing platform or a customer service chatbot. Rather than imposing identical obligations on every AI developer, the UK has empowered existing regulators to apply established legal principles within their respective domains.
For businesses, this means compliance depends not only on the AI itself but also on where and how it is deployed.
A fintech platform may need to satisfy expectations from the Financial Conduct Authority (FCA), while a recruitment platform processing applicant data falls primarily under the Information Commissioner’s Office (ICO). Competition concerns may involve the Competition and Markets Authority (CMA), whereas communications platforms may engage Ofcom.
The result is a governance ecosystem rather than a single rulebook.
The AI Safety Institute: Setting the Tone Rather Than Writing the Law
One institution has become central to Britain’s international AI strategy: the AI Security Institute (formerly the AI Safety Institute).
Established following the UK’s landmark AI Safety Summit, the institute focuses primarily on evaluating the capabilities and risks of advanced frontier AI systems. Rather than acting as a regulator, it provides technical expertise, conducts model evaluations and collaborates with leading AI developers on safety testing.
Its influence extends well beyond frontier models. By developing methodologies for evaluating AI reliability, robustness and misuse risks, the institute is gradually shaping wider industry expectations regarding responsible development.
For software startups, this represents an important shift. Safety is no longer viewed solely as an ethical aspiration; increasingly, it forms part of commercial due diligence conducted by enterprise customers and investors.
Data Protection Remains the Foundation
Many founders assume AI regulation begins with model transparency or algorithmic bias. In reality, for most UK businesses the first regulatory checkpoint remains data protection.
The Information Commissioner’s Office has consistently emphasised that organisations developing AI systems must continue to comply with UK data protection law whenever personal information is processed. Recent updates following the Data (Use and Access) Act 2026, which received Royal Assent in June, reinforce that AI systems are not exempt from long-standing obligations surrounding lawfulness, fairness, transparency and accountability.
For founders building generative AI applications, this has practical implications from the earliest stages of product development.
Questions such as these now form part of routine compliance assessments:
- Where does the training data originate?
- Does the organisation possess a lawful basis for processing personal data?
- Can users understand how AI influences decisions?
- Is only the minimum necessary personal information collected?
- Can individuals exercise their legal rights regarding their information?
These are no longer abstract legal concepts. They increasingly determine whether enterprise procurement teams approve AI-powered software.
Transparency Is Becoming a Competitive Advantage
One recurring theme throughout UK regulatory guidance is transparency.
Businesses deploying AI should be able to explain, in understandable language, when customers are interacting with automated systems, what personal information is being processed and how significant decisions are reached.
This does not require revealing proprietary algorithms or exposing commercially sensitive intellectual property. Rather, organisations must ensure users understand the role AI plays within the service they receive.
Transparency also extends internally.
Senior management should understand which AI models are being used across the organisation, where those models obtain information and what safeguards exist if outputs prove inaccurate.
For growing SaaS companies, maintaining an internal AI inventory is rapidly becoming recognised as good governance rather than administrative bureaucracy.
Accountability Cannot Be Delegated to the Algorithm
Perhaps the most misunderstood aspect of AI governance concerns responsibility.
Some founders continue to describe problematic outputs as “the AI made the mistake.”
Regulators reject this reasoning.
Whether an organisation develops its own foundation model or integrates commercially available APIs from providers such as OpenAI, Anthropic or Google, responsibility for deployment ultimately remains with the business placing the technology into service.
This principle influences procurement contracts throughout the UK technology sector.
Enterprise customers increasingly request documented governance procedures before signing agreements involving AI-enabled software. Questions surrounding human oversight, audit trails, incident response and model monitoring frequently appear alongside traditional cybersecurity assessments.
Consequently, governance has become a market differentiator rather than merely a compliance obligation.
Security Is No Longer Just About Cybersecurity
Artificial intelligence introduces entirely new categories of security risk.
Traditional cybersecurity focused primarily on protecting infrastructure against unauthorised access.
AI systems require additional safeguards.
Model inversion attacks, prompt injection, training data leakage and malicious manipulation of autonomous agents represent emerging threats that many organisations had not previously encountered.
The ICO’s updated AI guidance highlights the importance of security-by-design and data minimisation, encouraging organisations to adopt privacy-preserving techniques while protecting AI systems against novel attack vectors.
As AI agents gain greater autonomy across enterprise workflows, these risks become increasingly operational rather than theoretical.
The Compliance Playbook: Eight Governance Priorities for AI Founders
While every AI business faces unique regulatory considerations, several governance practices have emerged as essential across virtually every sector. Implementing these measures early not only reduces legal risk but also strengthens customer confidence and improves investment readiness.
1. Appoint Clear AI Accountability
One of the most common governance failures is the assumption that AI responsibility belongs exclusively to engineering teams.
It does not.
Every organisation deploying AI should identify an individual or governance committee responsible for overseeing AI use across the business. This does not necessarily require a Chief AI Officer. For many growing SaaS companies, accountability may sit with a CTO, Chief Product Officer or Data Protection Officer, depending on organisational structure.
The important point is clarity.
When enterprise customers ask, “Who is responsible for your AI governance?”, there should be a clear answer.
2. Maintain an AI Register
Many organisations already maintain asset registers covering software licences, cybersecurity infrastructure and personal data processing activities.
AI deserves the same treatment.
A practical AI register should document:
- every AI model used across the organisation;
- whether it is internally developed or supplied by a third party;
- the business purpose of each model;
- the categories of data processed;
- potential risks associated with deployment; and
- the safeguards implemented to mitigate those risks.
This register becomes invaluable during customer due diligence, security audits and regulatory enquiries.
3. Conduct AI Risk Assessments Before Deployment
One of the defining characteristics of the UK’s regulatory philosophy is proportionality.
Not every AI application presents the same level of risk.
An internal meeting-summary assistant poses significantly fewer governance challenges than an AI system screening job applicants or recommending insurance premiums.
Founders should therefore assess risk before deployment by considering:
- the potential impact on individuals;
- whether automated decisions could materially affect someone’s rights or opportunities;
- whether sensitive personal data is processed;
- the likelihood of inaccurate or discriminatory outcomes; and
- the availability of meaningful human oversight.
This assessment should become a standard stage within product development rather than an afterthought before launch.
4. Embed Human Oversight
The UK’s regulatory environment consistently reinforces one principle: AI should support human decision-making, not replace accountability.
For higher-risk applications, organisations should ensure humans remain capable of reviewing significant decisions, intervening where necessary and overriding incorrect outputs.
Human oversight is particularly important in sectors such as healthcare, financial services, employment and public services, where automated decisions may have substantial consequences for individuals.
The objective is not to eliminate automation but to ensure humans retain meaningful control.
5. Monitor AI Performance Continuously
Launching an AI model is not the end of governance.
Performance should be monitored throughout its operational life.
Models may drift over time as customer behaviour changes, datasets evolve or external conditions shift.
Businesses should therefore establish regular monitoring covering:
- accuracy;
- hallucination rates where applicable;
- bias indicators;
- customer complaints;
- security incidents; and
- model updates introduced by external providers.
Increasingly, enterprise procurement teams expect evidence that monitoring occurs rather than assuming models remain reliable indefinitely.
6. Strengthen Third-Party Vendor Oversight
Few startups build every component themselves.
Most rely on APIs, foundation models and cloud infrastructure supplied by external vendors.
However, outsourcing technology does not outsource responsibility.
Founders should understand:
- where suppliers process data;
- how providers manage security;
- whether models are trained using customer inputs;
- contractual responsibilities following model failures; and
- business continuity arrangements should providers experience service disruption.
Vendor governance is becoming an increasingly important component of AI assurance programmes.
7. Document Everything
Regulators often distinguish between organisations that make mistakes and organisations unable to demonstrate responsible decision-making.
Documentation therefore becomes a strategic asset.
Businesses should maintain records covering:
- governance decisions;
- testing procedures;
- bias assessments;
- security controls;
- human review processes;
- model changes; and
- incident responses.
Documentation does not prevent regulatory scrutiny—but it significantly improves an organisation’s ability to demonstrate responsible governance.
8. Prepare for Cross-Border Compliance
Although the UK has not replicated the EU AI Act, many British software companies operate internationally.
A London-based SaaS platform serving customers in Germany, France or the Netherlands may still fall within the scope of European legislation.
Likewise, multinational enterprise customers increasingly expect suppliers to demonstrate compliance with internationally recognised governance frameworks, regardless of legal jurisdiction.
For founders, this means designing governance that can satisfy multiple regulatory environments rather than treating UK compliance as the only consideration.
The Procurement Reality
Many founders continue to view AI governance as something regulators may ask about in the future.
The market has moved faster than regulation.
Today, procurement teams frequently ask vendors to complete AI-specific questionnaires before contracts are signed.
Common questions include:
- Do you use customer data for model training?
- Can users opt out of AI-assisted processing?
- How are hallucinations mitigated?
- Are high-risk decisions subject to human review?
- How are prompts and outputs secured?
- Is there an internal AI governance policy?
- How frequently are models evaluated?
For startups seeking contracts with banks, insurers, healthcare providers or government bodies, satisfactory answers to these questions increasingly determine whether commercial negotiations progress.
Governance, therefore, is becoming a sales enabler as much as a compliance requirement.
What Investors Are Looking For
Investor expectations have also evolved.
Two years ago, venture capital firms focused primarily on whether founders had integrated generative AI into their products.
In 2026, conversations have become considerably more sophisticated.
Investors increasingly examine:
- governance maturity;
- intellectual property ownership;
- data provenance;
- regulatory exposure;
- cybersecurity resilience;
- explainability; and
- operational risk.
Companies capable of demonstrating structured governance frequently inspire greater confidence than competitors relying solely on technical innovation.
This reflects a broader market recognition that sustainable AI businesses require robust governance alongside capable engineering.
Looking Ahead
The UK’s AI regulatory landscape continues to evolve.
The Government has indicated that additional legislation may emerge in the coming years, particularly regarding frontier AI models and copyright, while maintaining its commitment to supporting innovation. Rather than adopting a single comprehensive AI statute, policymakers continue to refine existing regulatory mechanisms and strengthen coordination between sector regulators.
For founders, waiting until future legislation arrives would be a mistake.
Many of the governance expectations shaping enterprise procurement today derive not from new AI-specific laws but from long-established obligations surrounding privacy, consumer protection, cybersecurity, equality and corporate accountability.
The businesses best positioned for long-term growth will be those that view AI governance not as a regulatory burden but as an operational capability.
Trust, after all, remains one of the most valuable competitive advantages any technology company can build.
Britain Times: Founder Compliance Checklist
Before launching an AI-enabled product in the UK, founders should be able to answer “yes” to the following questions:
✓ Have we identified who is accountable for AI governance?
✓ Do we maintain an inventory of every AI system used across the business?
✓ Have we assessed privacy, fairness and security risks before deployment?
✓ Can users understand when AI is influencing decisions?
✓ Is meaningful human oversight available where appropriate?
✓ Do we continuously monitor AI performance after launch?
✓ Have we assessed the governance standards of third-party AI suppliers?
✓ Can we demonstrate our governance decisions through documented evidence?
If the answer to any of these questions is “no”, organisations should regard that gap as a business priority rather than simply a legal issue.
Sources
- UK Department for Science, Innovation and Technology – Data (Use and Access) Act 2025 and commencement guidance.
- Information Commissioner’s Office – Guidance on AI and data protection and Data (Use and Access) Act 2025 implementation.
- UK Government – Data (Use and Access) Act 2025: data protection and privacy changes.
- From Turing to Tomorrow: The UK’s Approach to AI Regulation (2025), Oliver Ritchie, Markus Anderljung and Tom Rachman.
Editor’s Note
This article is written for founders, technology leaders and enterprise decision-makers seeking to understand the practical implications of the UK’s evolving AI governance landscape as of 15 July 2026. As legislation and regulatory guidance continue to develop, organisations should monitor updates from the Department for Science, Innovation and Technology (DSIT), the Information Commissioner’s Office (ICO) and relevant sector regulators.
Leave a Reply